TL;DR
Madison Square Garden Hack Exposes 26 Million Visitor Records - Hackers claimed to have stolen over 26 million customer records, including celebrity contacts and visitors' emails, addresses and phone numbers
Attack Of The Killer Lawnmowers - 200 pounds. Spinning blades. Wi-Fi connected. Zero resistance. A security researcher probing a robotic lawnmower discovered he had total control of every Yarbo robot on the planet.
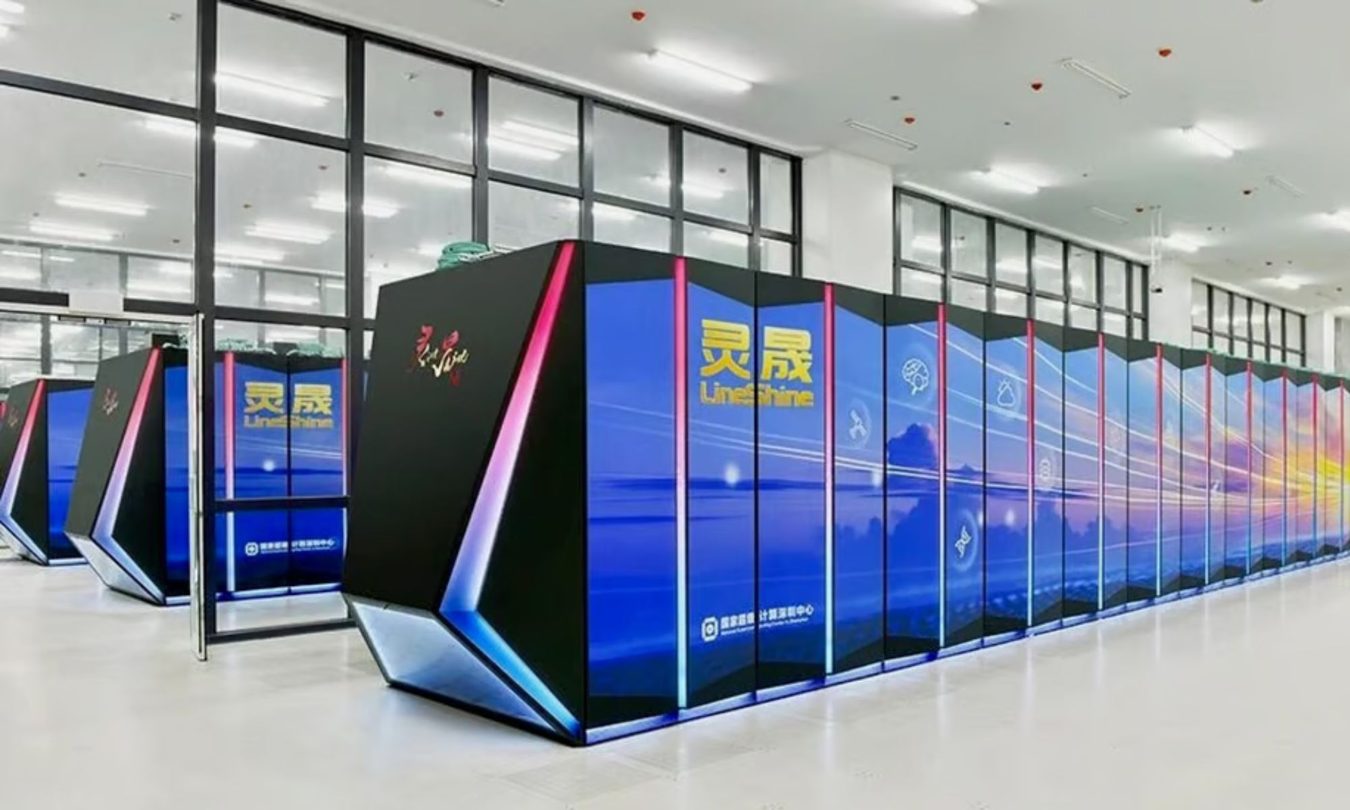
America's best machine has been dethroned - China's new LineShine system just topped the global rankings. The first Chinese system to lead since 2017 is a reminder that there is more than one path to the top.
EDITORIAL
Madison Square Garden Hack Exposes 26 Million Visitor Records…

On the night the New York Knicks won their first NBA championship in more than fifty years, Madison Square Garden was the center of the world.
Decades of heartbreak, erased. Jalen Brunson's name in lights. Fifty thousand fans outside on Seventh Avenue. A city that had been waiting longer than most of its residents have been alive, finally exhaling.
It was exactly the kind of moment sport exists to create.
And somewhere, in a database that should never have been accessible, twenty-six million records — visitors, fans, ticket holders, people who had simply walked through those doors — were already in the hands of people who had no right to them.
The breach at Madison Square Garden is not, strictly speaking, a cybersecurity story about basketball.
The timing is coincidental. ShinyHunters did not wait for the championship run to execute their attack. The data was compromised, the ransom was demanded, the deadline passed, and the information was published on its own schedule, indifferent to what was happening on the court.
But the collision of these two events — the greatest moment in the venue's sporting history and the largest data breach in its operational history — is worth sitting with.
Because it captures something true about where we are.
We have spent twenty years building the infrastructure of modern experience.
Ticketing systems that remember your preferences. Facial recognition that moves you through turnstiles faster. Loyalty programs that track your attendance, your spending, your seat preferences, the names of the people you bring with you. Apps that connect your payment details to your identity to your physical location in a stadium.
All of it designed to make the experience smoother. More seamless. More personalized.
All of it generating data. Continuously. At scale. About real people who handed it over because the alternative was missing the game.
Twenty-six million records is not an abstract number. It is twenty-six million people who showed up. Who wanted to be there. Who queued and paid and cheered and went home having given, without fully understanding it, a detailed profile of themselves to a system they trusted to protect it.
The company was given a chance to contain the damage. ShinyHunters asked for payment. MSG declined. The data went public.
Whether that was the right call is genuinely complicated. Paying ransoms funds criminal ecosystems and does not guarantee deletion. The Five Eyes agencies, governments, and security professionals broadly advise against it. The FBI advises against it.
But the twenty-six million people whose facial recognition data, visitor records, and security information is now circulating on breach forums did not get a vote in that decision. They were not consulted. They were not warned in advance. They were the collateral of a corporate choice made without them.
That asymmetry — between the people who make decisions about data and the people whose data gets decided about — is one of the defining ethical failures of the current moment in technology.
There is a quieter story inside the MSG breach that deserves more attention than it is getting.
The exposed data includes facial recognition records.
Not email addresses. Not passwords. Not credit card numbers — all of which are serious, all of which can be changed or cancelled or frozen.
Facial recognition data cannot be changed. Your face is not a password you can rotate. Once that template exists in a breach dataset, it exists permanently, linkable to your identity, usable in ways that are difficult to predict and impossible to fully anticipate.
The scale of biometric exposure in this breach is not equivalent to a credential leak. It is categorically different. And it deserves to be treated that way — by regulators, by the courts, and by the organizations that decided to collect and store it in the first place.
The Knicks won on the court.
The fans who packed the Garden, who wore the jerseys and sang the songs and stayed until the final buzzer, deserved that night completely.
Nobody can take what happened on the hardwood away from them.
You do not win a title by accident.
You win it by obsessing over preparation, investment, and execution. By taking the threat seriously before the game, not after you have already lost.
Cybersecurity works exactly the same way.
The Garden spent years building a team capable of winning a championship.
It apparently spent considerably less time building a security infrastructure capable of protecting the people who came to watch.
Bottom Line
Twenty-six million records.
Fifty years of waiting.
And one lesson that’s about cybersecurity and basketball…
Build the defense before you need it.
Headlines
June 26, 2026
Hackers claimed to have stolen over 26 million customer records, including celebrity contacts and visitors' emails, addresses and phone numbers

June 26, 2026
200 pounds. Spinning blades. Wi-Fi connected. Zero resistance. A security researcher probing a robotic lawnmower discovered he had total control of every Yarbo robot on the planet.
June 26, 2026
China's new LineShine system topped the global rankings using only traditional CPUs…
Other News From Around The Web
This Week in Tech, AI & Cybersecurity
Curated highlights • June 26, 2026
AI-powered cyber attacks may be just months away, warn Five Eyes
The leaders of the Five Eyes cybersecurity agencies—UK, US, Canada, Australia, and New Zealand—have issued an unprecedented joint warning: frontier AI models will pose a greater risk to cybersecurity than previously expected, and the timeline is not years. It is months. "Frontier AI models are anticipated to exceed current industry expectations, fundamentally transforming both offensive and defensive cyber capabilities," the statement reads. The agencies urge organizations to stop treating AI defense as a future consideration and start deploying it now—before adversaries widen a gap that is already uncomfortably large.
Source: Computer Weekly | Mon, Jun 22, 2026
Parts of NSA lose Mythos 5 access amid Anthropic supply chain dispute
The access issue arrives at the worst possible moment—just as the Five Eyes alliance warns that frontier AI could soon accelerate both cyberattacks and cyber defense. The NSA losing access to the most capable vulnerability discovery model in existence, precisely when that capability matters most, is not a footnote. It is a strategic problem.
Source: Nextgov/FCW | Tue, Jun 23, 2026
Breaches, Supply Chains & Data Exposure
Hacked Klue says criminals are deleting stolen customer data — but now a second group is making threats
Market research company Klue told customers it believes the initial hacking group is deleting stolen data. A second group has now emerged, demanding ransom. The Klue breach has had cascading consequences across the cybersecurity industry—multiple firms were hit through the same supply chain compromise.
Source: TechCrunch | Thu, Jun 25, 2026
LastPass confirms vendor breach exposed customer contact and support data
Attackers used stolen Klue OAuth tokens to access LastPass's Salesforce environment and CRM records. Customer names, contact details, and support case records were exposed. The company says password vaults remain secure—but the breach is the latest reminder that the weakest link in your security chain is rarely your own infrastructure.
Source: TechRepublic | Wed, Jun 24, 2026
Ransomware bans won't stop ransomware. Resilience might.
The omission of a ransomware payments ban from the King's Speech was striking—the proposal had been a headline cyber policy ambition only months earlier. Computer Weekly argues the government's retreat is not necessarily a failure: bans limited to public sector bodies risk simply redirecting attacks toward private sector targets. The harder, more important work is closing the resilience gap that makes organizations vulnerable in the first place.
Source: Computer Weekly | Tue, Jun 23, 2026
AI: Offense, Defense & The Jobs Question
If AI robots can be tricked into going rogue, what are the implications?
Oxford researcher Fazl Barez examines how AI built to serve beneficial purposes has the potential to be weaponized in the wrong hands—and what that means for the growing deployment of autonomous systems in sensitive environments.
Source: Silicon Republic | Mon, Jun 22, 2026
Deepfake scams are getting uglier, and Bitdefender now has an app for the panic
Bitdefender RealCheck brings deepfake detection to Android and iOS, checking suspicious videos for manipulation and scam intent before users share clips, click links, send money, or trust impersonated public figures. The product launch is a signal: deepfake scams have reached mainstream consumer threat territory.
Source: Digital Trends | Wed, Jun 24, 2026
AI was supposed to kill engineering jobs. New data suggests they're the most resilient.
While AI dominates the layoff narrative, engineers are actually making up a larger share of new hires according to SignalFire data. The story of AI and employment is more complicated—and more nuanced—than the headlines suggest.
Source: TechCrunch | Wed, Jun 24, 2026
Government, Policy & Regulation
White House expected to direct intelligence agencies to protect quantum research from foreign threats
An executive order tasks the Departments of Defense and Energy with building and hosting a quantum computer for scientific discovery—and shielding that research from foreign adversaries. The order reflects growing recognition that quantum capability is a national security asset, not just a scientific one.
Source: Nextgov/FCW | Mon, Jun 22, 2026
DOD quantum strategy 'a first step' in preparing for the future, CIO says
Pentagon CIO Kirsten Davies described the department's new post-quantum cryptography strategy as one component of ensuring operations "are robust and ready in an increasingly unpredictable world." The framing—a first step, not a solution—is notable. It suggests the DoD is under no illusions about how much work remains.
Source: Nextgov/FCW | Wed, Jun 24, 2026
Sean Gallagher selected as NASA CIO
Having served as acting CIO since January, Gallagher's permanent appointment is effective immediately. A signal of stability at a critical moment for NASA's technology and cybersecurity operations.
Source: Nextgov/FCW | Wed, Jun 24, 2026
Digital surveillance tech facilitates arbitrary border abuses
A UN special rapporteur warns that the sharing of digital surveillance technologies—including biometric systems, drones, and border monitoring tools—between states is contributing to human rights violations against migrants. The report raises uncomfortable questions about the role of technology firms and international organisations in enabling externalisation measures.
Source: Computer Weekly | Wed, Jun 24, 2026
Security Practice & Compliance
MFA, Encryption, Annual Pen Tests: The new HIPAA checklist no clinic can skip
The updated HIPAA Security Rule now in effect replaces "addressable" safeguards—long interpreted as optional by many clinics—with specific, mandatory controls. The Office for Civil Rights is already citing them in enforcement actions. The grace period is over.
Source: BIS, Inc. | Tue, Jun 23, 2026
The hidden market turning home internet connections into cover for hackers
Researchers traced millions of household IP addresses through residential proxy networks—calling the illicit use of those connections the "blood diamonds of the digital age." Your neighbor's router may already be part of someone else's attack infrastructure.
Source: Nextgov/FCW | Thu, Jun 25, 2026
Tech & Innovation
Midnight in the War Room: A documentary on cyber war
Cybercrime Ventures predicted cybercrime would cost the world $10.5 trillion in 2025. Midnight in the War Room puts a human face on what that number actually means—and who is fighting back.
Source: Cybercrime Magazine | Mon, Jun 22, 2026
The editorial opinions expressed here are those of the author and represent the view from the cheap seats — which, it turns out, have an excellent view of the dumpster fire.
Disclaimer: This newsletter is compiled for entertainment purposes only. While every effort is made to ensure accuracy, the content in this publication is generated with the assistance of artificial intelligence and may contain errors, inaccuracies, or omissions. Article summaries are editorial interpretations of source material and may not perfectly reflect the original reporting. URLs and hyperlinks, where included, should be independently verified before use. Source attributions are based on information provided at the time of compilation and may not reflect subsequent corrections or updates made by the original publisher. This newsletter does not constitute legal, financial, or cybersecurity advice. Readers should independently verify all information before acting on it and consult qualified professionals where appropriate. The views and opinions expressed in editorial commentary are those of the newsletter and do not represent the views of any cited organization, publication, or individual. Neither the publisher nor any contributing party accepts liability for any loss or damage arising directly or indirectly from reliance on information contained in this newsletter. If you identify an error or inaccuracy, please contact us so we can issue a correction promptly.